
Loading...
Every organization faces a different threat landscape. AVENTIQ adapts its approach to the technology, risk profile, and operational requirements of each business.
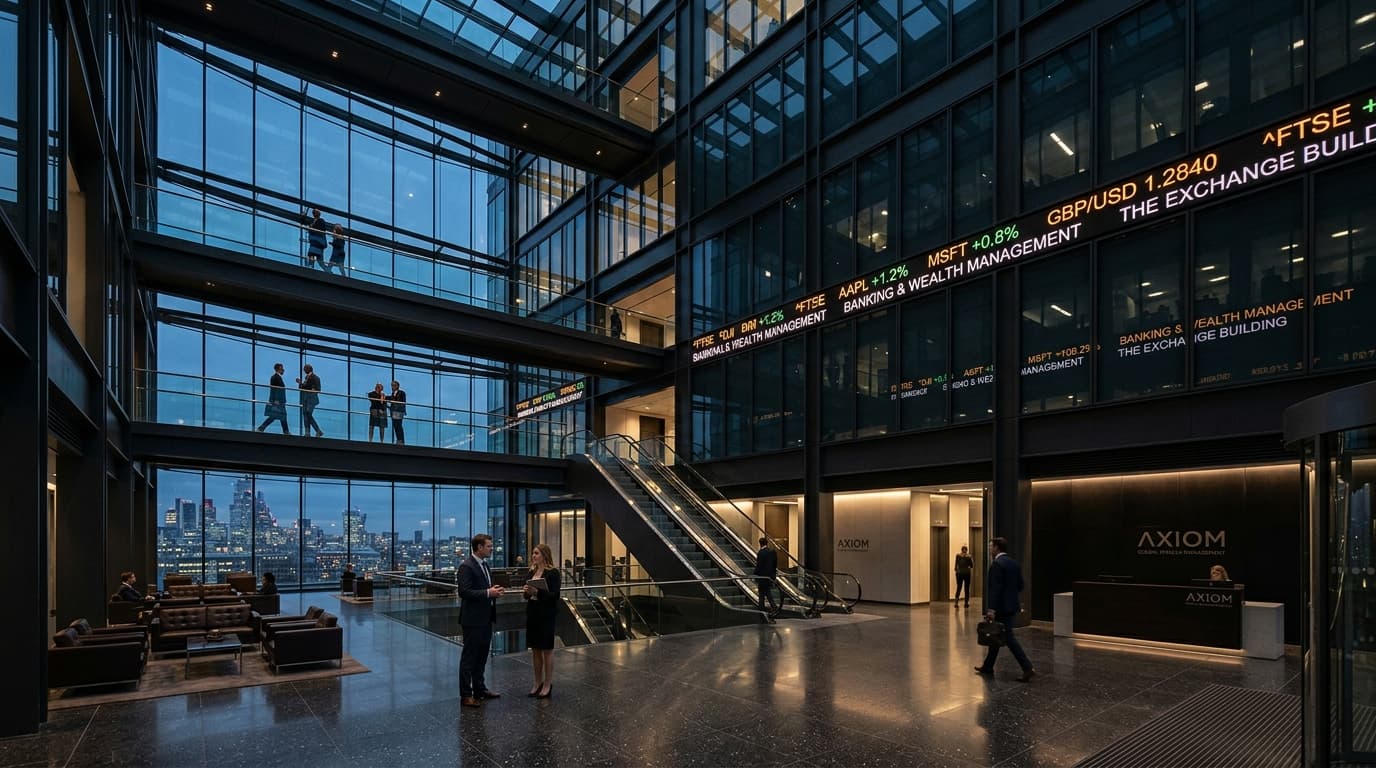
Comprehensive penetration testing, rigorous identity access controls, and adherence to established financial security standards.
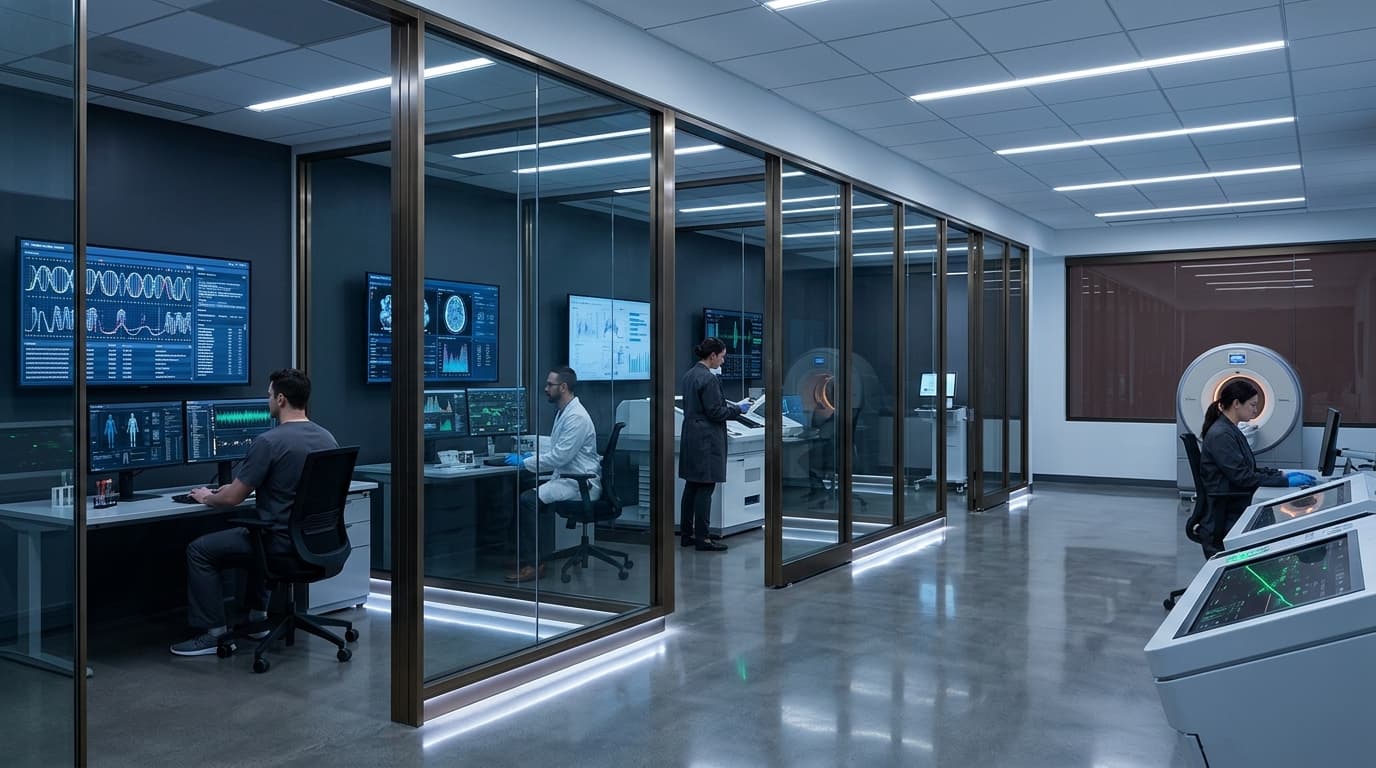
Strict network segmentation, endpoint hardening, and rapid-response incident preparation to maintain patient care continuity.
Deep offensive penetration testing, cloud posture validation, and secure developer configuration assessments.
Web application security reviews, robust mail filtering against impersonation, and continuous vulnerability verification.
Air-gapped and segmented network architecture reviews, server hardening, and clear incident recovery playbooks.
Standardized branch infrastructure hardening, centralized identity governance, and strict perimeter controls.
Microsoft 365 hardening, robust DMARC/anti-spoofing controls, and multi-factor authentication enforcement.
High-impact, practical baseline assessments, turnkey Microsoft 365 hardening, and essential threat prevention.
GRC gap assessments, actionable remediation plans, and independent third-party security validation.